Your nonprofit must implement 10 core PIPEDA safeguards: obtain consent for donor and beneficiary data collection, limit collection to necessary information only, protect data with encryption and access controls, retain records for CRA’s minimum seven years, establish breach response procedures, appoint a privacy officer, document all policies, train staff and volunteers, conduct annual privacy audits, and ensure third-party vendors (payment processors, donor management systems) meet equivalent standards.
Why Does PIPEDA Apply to Your Nonprofit When You’re Not a Business?
You collect credit card information during fundraising campaigns. You store beneficiary health records, income details, and family circumstances. You maintain volunteer background checks and employment records. The moment your nonprofit handles personal information in the course of commercial activities—including donation processing, event ticket sales, or charitable receipts—PIPEDA applies to you exactly as it does to for-profit businesses.
BC’s PIPA legislation sets a higher bar. If your Victoria nonprofit serves BC residents, you must meet PIPA’s stricter consent and notification requirements, not just federal PIPEDA minimums. This catches many organizations off guard during their first CRA audit or when a donor asks to see what information you hold about them.
The confusion stems from the charitable mission. Board members assume privacy laws exempt nonprofits focused on community good. They don’t. Your donor management system holds the same sensitive payment data as any retailer. Your client files contain more intimate details than most businesses ever see.
Grant funders now require proof of compliance. United Way applications ask for cybersecurity attestations. Community foundation grants require documented data protection policies. BC Gaming Policy and Enforcement Branch audits your financial record-keeping systems. You can’t access restricted funding without demonstrating you protect the information those funds help you collect.
What Happens If Your Nonprofit Ignores Privacy Requirements?
A data breach triggers mandatory reporting to the Privacy Commissioner and affected individuals under PIPEDA. Your organization’s name appears in public breach databases. Donors see headlines about exposed credit card information. Monthly giving programs collapse as trust evaporates.
CRA audits reveal you can’t produce required digital records because backup systems failed months ago. Without seven years of compliant records, you risk charitable status. Losing that status means donors can’t claim tax receipts. Your funding model disintegrates.
BC Gaming grant applications get rejected because you can’t provide the required cybersecurity documentation. That $50,000 in gaming funds you budgeted for program delivery never arrives. You’re explaining to your board why technology gaps cost the organization restricted funding that took months to apply for.
A volunteer accidentally emails a beneficiary list with health conditions to the wrong recipient. Under PIPA, you must notify everyone affected. Legal fees for breach response and potential penalties come from operating reserves—money that should fund your mission. The philosophical wrong cuts deepest: people trusted you with their most vulnerable information to get help, and you failed to protect them.
The Privacy Commissioner of Canada can impose penalties up to $100,000 per violation for organizations that fail to implement reasonable security safeguards.
What Are the 10 Core PIPEDA Safeguards Your Nonprofit Must Implement?
1. Consent Management: You need explicit, documented consent before collecting donor credit card information, beneficiary health records, or volunteer background checks. “By donating you agree to our privacy policy” buried in fine print doesn’t meet the standard. Consent must be clear, separate, and specific to each type of data collection.
2. Collection Limitation: Only gather information directly necessary for the stated purpose. If you’re processing a one-time donation, you don’t need the donor’s employment history. If you’re scheduling a volunteer, you don’t need their medical records. Every field in your forms must justify its existence.
3. Use and Disclosure Restrictions: Data collected for grant applications can’t be repurposed for fundraising appeals without new consent. Beneficiary information can’t be shared with partner organizations without explicit permission. Your donor list isn’t an asset you can sell or trade, even to similar charities.
4. Data Accuracy: You must keep records current and correct. Sending tax receipts to outdated addresses or contacting deceased donors because your database wasn’t updated violates PIPEDA and damages your reputation. Establish regular data cleaning schedules.
5. Retention Limits: CRA requires seven years of financial records for registered charities, but that doesn’t mean keeping volunteer applications from 2005. Define retention periods for each data type, then delete information when the purpose expires and legal minimums are met.
6. Security Safeguards: Encryption for data in transit and at rest. Password protection for donor databases. Access controls so volunteers can’t view financial records. Physical security for paper files containing beneficiary information. Regular security updates for your donor management system. Backup systems that actually work when you need them.
7. Transparency and Access: Any donor or beneficiary can request to see what information you hold about them. You have 30 days to respond under PIPA. That means you need systems organized well enough to actually find and compile an individual’s records across your database, email archives, and paper files.
8. Privacy Officer Appointment: Someone must be accountable. Even a small nonprofit needs a designated person responsible for privacy compliance, breach response, and access requests. This can’t be “whoever answers the phone.” It needs to be documented, with clear authority and resources.
9. Breach Response Procedures: Written plans for what happens when a laptop with donor data gets stolen or a volunteer accidentally emails sensitive beneficiary information to the wrong person. Who gets notified? How fast? What gets documented? You don’t want to figure this out during a crisis.
10. Third-Party Vendor Compliance: Your payment processor, donor management system vendor, email marketing platform, and cloud backup provider all handle your data. Their security failures become your PIPEDA violations. Contracts must require equivalent privacy protections and give you audit rights.
Chris Wilkinson described his experience with technology service providers: “Luke and his team at DataStream Networks are honestly amazing! The speed of the leader, the speed of the pack ‘they say’…and Luke sets the tone for how great his team is. First off, he cares so much about his team. Second, the DataStream team understands what it takes to provide authentic & wonderful customer service. Third, the whole team is deeply committed to service delivery and quality, including the latest greatest tech.” When your donor system crashes three days before year-end campaign processing, that speed and commitment to service delivery becomes the difference between meeting compliance deadlines and watching donation revenue evaporate.
How Do You Implement These Safeguards Without a Full-Time IT Person?
Start with a gap analysis. Document what personal information you actually collect, where it’s stored, who can access it, and how it’s protected right now. Most Victoria nonprofits discover donor credit card numbers in old spreadsheets, beneficiary files on personal laptops, and volunteer records in unsecured shared drives.
Prioritize based on sensitivity and volume. Credit card data and beneficiary health records demand immediate encryption and access controls. Volunteer contact information, while still protected under PIPEDA, presents lower risk. Focus your limited resources where breach consequences hit hardest.
Automate what you can. Modern donor management systems include consent tracking, retention schedules, and access logging. Email encryption can be automatic. Backup systems should run without human intervention. Technology removes the compliance burden from stretched staff.
Your board needs one-page policies they can actually approve and staff can actually follow. A 47-page privacy manual nobody reads fails the “reasonable safeguards” test. Clear, specific procedures for common scenarios—processing donations, handling beneficiary intake, managing volunteer records—work better than theoretical frameworks.
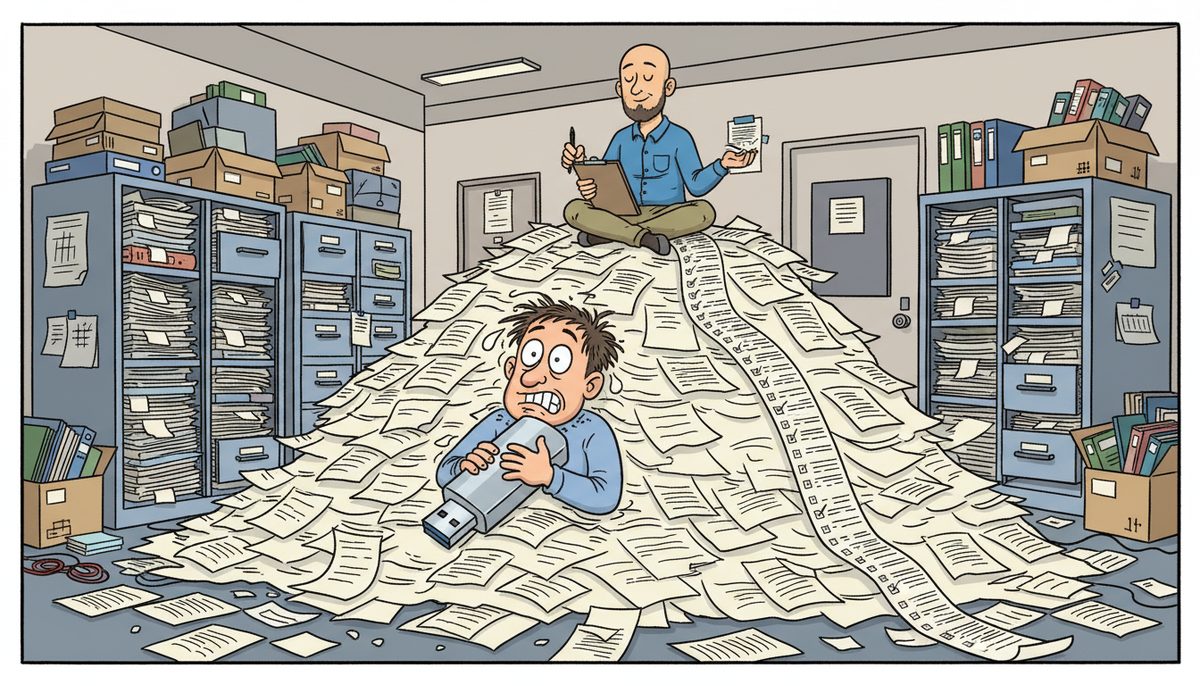
Train everyone who touches data, including volunteers. The retired accountant helping with bookkeeping needs to understand why donor files can’t go home on a USB stick. The summer student processing donations needs to know that credit card numbers never get written down or emailed. Annual training isn’t optional.
Test your systems before you need them. Can you actually restore last month’s donor database from backup? Can you compile one person’s records in response to an access request? Can you execute your breach response plan when your executive director is on vacation? Run drills.
For Vancouver Island nonprofits, local support matters during compliance crises. When BC Gaming audits your financial systems or a grant deadline requires cybersecurity documentation, waiting for mainland technicians to catch the ferry costs you funding opportunities. Organizations need IT support in Victoria that understands both nonprofit technology constraints and BC’s specific privacy requirements.
When Should Your Nonprofit Bring In Outside Help for Compliance?
You’re facing a CRA audit and can’t produce seven years of compliant digital records. Your current backup system hasn’t been tested in three years, and you’re not sure if restoration actually works. That’s a compliance emergency requiring immediate professional intervention.
Your donor management system vendor notifies you of a security breach affecting customer databases. Under PIPEDA, you have specific notification timelines and reporting requirements. You need breach response expertise immediately, not after you’ve missed legal deadlines.
A major grant application requires cybersecurity attestations and documented data protection policies you don’t have. The funding opportunity is worth $75,000, but the application deadline is six weeks away. You need rapid policy development and system documentation.
Your board asks questions you can’t answer: “How do we know donor credit card information is encrypted?” “What happens if someone requests to see their data?” “Are we actually compliant with PIPA?” When governance oversight reveals knowledge gaps, you need assessment and remediation.
The anxiety of handling sensitive donor credit card information and beneficiary data without a full-time IT person is real. You wonder if you’re meeting PIPA requirements or risking everything. Victoria nonprofits get stuck waiting for mainland technicians during BC Gaming grant deadlines while board members ask why technology problems are threatening funding.
Since 2012, DataStream Networks has served Vancouver Island organizations with local technicians in Victoria, Nanaimo, Duncan, and Cobble Hill who understand nonprofit technology and compliance needs. When you call, live people answer immediately—no voicemail, no phone trees, no waiting while grant deadlines approach. Most problems get fixed remotely within minutes, and when on-site work is needed, a local technician arrives without ferry delays.
Getting your nonprofit compliant follows three clear steps:
- Call (250) 929-0745 and talk to a real Victoria technician immediately who understands nonprofit compliance requirements and BC’s PIPA standards
- Get your donor system, backup, or security gaps diagnosed with a compliance assessment that identifies exactly what needs fixing and what’s already working
- Implement the specific safeguards your organization needs—encryption, access controls, backup systems, policy documentation—with local support that keeps your systems running through fundraising campaigns and grant deadlines
What Does Success Look Like for a PIPEDA-Compliant Nonprofit?
You process December year-end donations confidently, knowing donor credit card data is encrypted, consent is documented, and CRA-compliant records are automatically backed up. When the inevitable spike in giving hits, your systems handle the volume without security shortcuts.
Grant applications get submitted on time with required cybersecurity attestations already in place. United Way and community foundation reviewers see documented data protection policies that meet their standards. BC Gaming audits find financial record-keeping systems that comply with their requirements. You compete for restricted funding on program merit, not technology gaps.
A donor requests to see what information you hold about them. Your privacy officer pulls the records in 20 minutes, responds within PIPA’s 30-day window, and the donor comments on how professional and organized your nonprofit appears. Trust deepens instead of eroding.
Your board sleeps soundly knowing sensitive beneficiary information meets PIPA standards, breach response procedures exist and have been tested, and the organization’s charitable status isn’t at risk from compliance failures. Technology protects your mission instead of threatening it.
If your donor database, backup systems, or privacy policies keep you awake wondering if you’re actually compliant, call (250) 929-0745 to talk to a real technician now. Your nonprofit’s compliance gaps can be fixed faster than you think when you’re working with people who understand both the technology and the stakes.
Frequently Asked Questions
Does PIPEDA apply to small nonprofits with limited donor data?
Yes, PIPEDA applies to any nonprofit conducting commercial activities like processing donations, selling event tickets, or issuing charitable tax receipts, regardless of organization size. BC’s PIPA sets even stricter standards for nonprofits serving BC residents. The volume of data doesn’t determine compliance requirements—the sensitivity and nature of information collected does, meaning even small organizations handling donor credit cards or beneficiary records must implement reasonable safeguards.
How long must nonprofits retain donor and financial records under PIPEDA?
CRA requires registered charities to retain financial records, including donation documentation, for a minimum of seven years from the end of the tax year they relate to. Under PIPEDA, you must delete personal information once the purpose for collection expires and legal retention minimums are met. This means keeping donor tax receipt records for seven years, then securely deleting them unless ongoing consent exists for other purposes like continued fundraising communications.
What counts as a reportable data breach for nonprofits under PIPEDA?
You must report breaches to the Privacy Commissioner and affected individuals when there’s a real risk of significant harm—typically when sensitive information like credit card numbers, health records, or financial details are exposed. A stolen laptop with encrypted donor files may not require reporting; an unencrypted laptop or accidentally emailed beneficiary list with health conditions likely does. You must maintain breach records even when notification isn’t required, documenting the incident, response, and remediation steps taken.
Can nonprofits share donor information with partner organizations or fundraising platforms?
Only with explicit consent that clearly identifies the third parties receiving information and the purposes for sharing. Your privacy policy must disclose these partnerships upfront. Sharing donor lists with similar charities, selling contact information, or allowing fundraising platforms unrestricted data access without specific consent violates PIPEDA. Third-party contracts must require equivalent privacy protections, and you remain accountable for their handling of your donors’ and beneficiaries’ information even after it’s shared.
What happens if a nonprofit volunteer accidentally exposes beneficiary data?
You must assess the risk of significant harm and determine if breach notification is required under PIPEDA. Document the incident immediately: what information was exposed, to whom, how many people affected, and what remediation steps you took. Notify your privacy officer and potentially the Privacy Commissioner and affected individuals depending on sensitivity. This is why volunteer training and access controls matter—preventing accidental exposure through clear procedures and technical safeguards protects both beneficiaries and your organization from breach response costs and reputational damage.